Pages

Showing posts with label Linux. Show all posts

Thursday, May 10, 2012

Eject the Warp Core: A practical look at filesystem segregation and encryption.

Here's my presentation I gave at Ohio InfoSec Forum today about the "Ejectable Core Backtrack Machine" and how filesystem segregation and encryption can help keep your data out of the wrong hands.

To get the full experience, open up the speaker notes to read along with what I'll be saying. It won't replace actually being there, but hopefully it'll help you grasp the concepts.

Future considerations (from InfoSec):

  • tmpfs instead of /tmp
  • Find a way to disable direct memory access on the kernel level (firewire and PCI can exploit this)


Monday, August 15, 2011

Chrome OS Bootable Flash Drive! (Built on: 8/9/2011)


New version! I'm also cleaning up all of the old versions and linking them to this page. This version is very very cool, lots of new ideas and features. Chrome OS is really coming into its own, you can see Google's new design team hard at work here. Check it out!


Credits and Utilities:
To unpack this file, you will need the totally awesome and free unzipping utility: 7zip
This pack contains the Image Writer for Microsoft Windows, which is a great, simple way to take or place images onto drives. Give these guys a hand!
Instructions are included in a text file in the download!

Tuesday, June 7, 2011

Chrome OS Bootable Flash Drive! (Built on: 6/7/2011)


Another version! Its been quite a while since I've put one of these out, so I figured it would help everyone if I released an updated version. As usual, all instructions are included in the download, so pull it down and give it a shot. Chrome OS is really growing up, and fast. I'm really excited for the future of Chrome OS and cloud-based computing in general. This is the future and it is now.

Chrome OS - 060711.7z
Chrome OS - 061311.7z

Update: Looks like there were a few nasty bugs with the June 7th build, I've rebuilt with newer sources in an attempt to give you a more stable build. Enjoy!

Update 2: Looks like the 6/13 build has some major GUI bugs and stability issues. Here's the main point: These are daily builds, nasty bugs happen. I'll wait a bit before releasing the next daily build, see what happens from there. I've re-included the link to the previous version, as it is a bit more stable.

Credits and Utilities:
To unpack this file, you will need the totally awesome and free unzipping utility: 7zip
This pack contains the Image Writer for Microsoft Windows, which is a great, simple way to take or place images onto drives. Give these guys a hand!
Instructions are included in a text file in the download!

Monday, January 17, 2011

Server-Bits #10: Subversion

Subversion! One of the best ways to keep track of versions for code, homework, various essays, you name it. If it changes and you want the ability to roll back changes, Subversion is for you. In reality, Subversion is one of many types of versioning software out there, but its the one we are going to cover in this tutorial. If you're really interested in the alternatives, Google around for: Git, Mercurial, among many other smaller projects.

Why would anyone want to set up a software repository? Easy answer if you're a programmer of any sort. I'm a hobbyist programmer, and I constantly break my own code and projects when trying new things. I wanted an easy way to roll back any changes that I had made, while still retaining a history of some sort. I initially did this by copying different versions of the code into different folders, but this proved to be unmanageable in the long run. At the time, I was using 6 different computers to write my code, depending on which location I was in during that day. Manually copying this folder to a USB stick, then re-syncing the changes became a major hassle. Subversion allows you to create a repository in a folder and commit changes to it. Want to update a particular machine with the latest version of the code? Easy, subversion has an update feature that only pulls down the changes of the file since you last synced. Easy stuff, and I'll show you how to build your own subversion repository.


Tuesday, December 21, 2010

Cloudbound: The CR48 (Part 2)


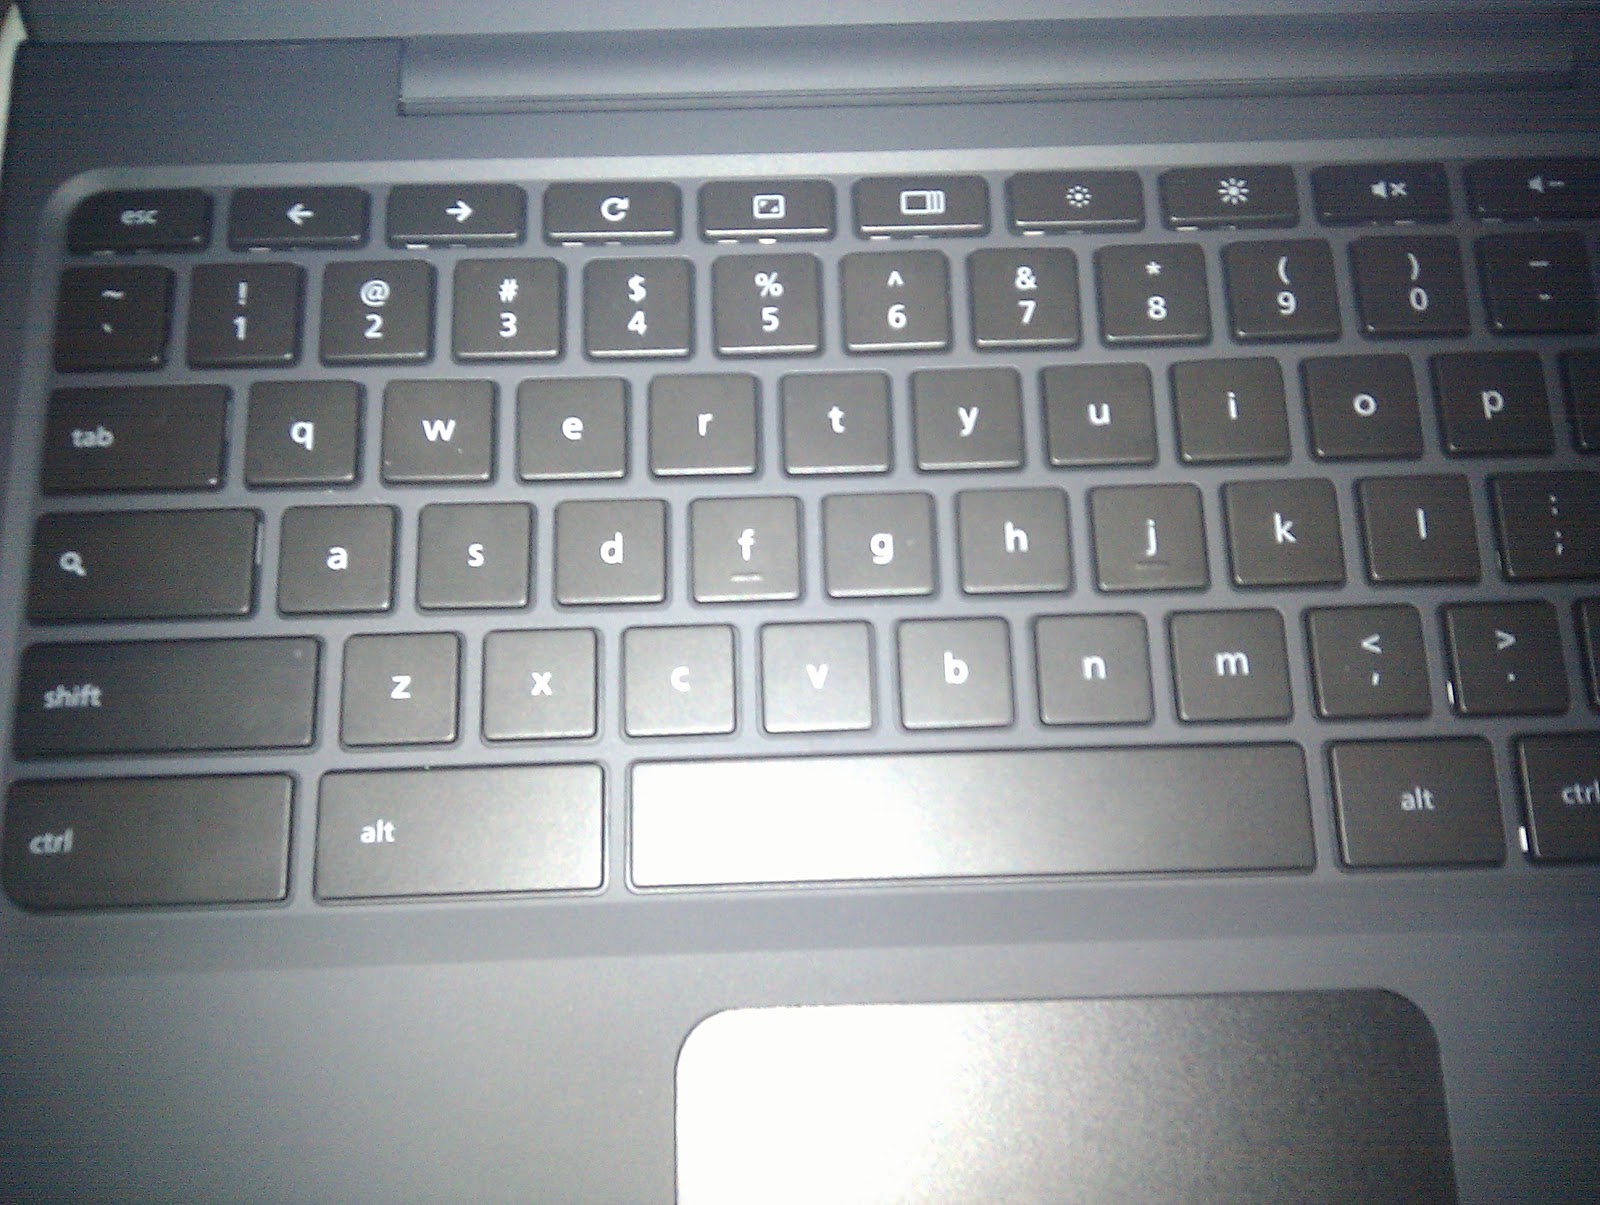
The CR48 notebook itself is sleek, simple, and unbranded. Completely unbranded. No logos anywhere. Just a matte black notebook with a rubbery feel. To be honest, reviewing the hardware doesn’t really make much sense. The purpose of this pilot program isn’t to review the laptop that some company made on contract, the point is to review and bugtest the software.
But the readers want to know, just how is the CR48? In a word: Amazing. Like the Nexus One, the CR48 embodies the essence of what Google thinks is possible with a Chrome OS notebook. Simple, from the keyboard to the case, the CR48 is the essence of software driving hardware. Not one logo is shown on the device in any form. Not even an informational sticker or set of warning labels. This is a tool for developers through and through. Honestly, I wish all notebooks were built this cleanly.


A small compliant so far, the battery doesn’t quite fit 100% snug to the bottom of the case on one corner. Not a deal breaker by any means, but this shows that the company Google hired is still working out the kinks in the manufacturing process. Granted, this is alpha-hardware, and never meant to be sold to the general public in this form, so I really have no reason to complain.
All in all, I really love the simplicity, long battery life, and light weight, easy to carry shape of this build. If this is the template for Chrome OS notebooks, its about to be a very good year for Google. The next post I have lined up is a general overview of Chrome OS, then feature highlights and more in-depth views, including bugs. Stay tuned!

Thursday, December 16, 2010

Cloudbound: Chrome OS Introduction (Part 1)

Welcome to Cloudbound! My brand new blog category dealing with all things Chrome OS and CR48. As some of you may know already (full disclosure here), I am now part of Google's official beta-tester group for Chrome OS and CR48. Before I get into the specifics, let me go over exactly what Chrome OS and CR48 are, just in case you are new to the game.

Chrome OS is a Linux-based operating system made by Google for cloud computing devices. My, oh my, what a buzz word. Cloud computing. What is it exactly? I can guarantee that most of you do some form of cloud computing each and every day.

Cloud computing is using applications and storage on the internet instead of on your local computer. Ever upload a picture to Facebook, Picasa, or Flickr? You’re using the internet to store those pictures, you are using cloud computing! Ever use Google Docs to type up a paper? That’s another example of cloud computing. Ever listen to music on Pandora, watch a television show on Hulu, or upload a video to YouTube? Those are all great examples of cloud-based media services.
So why make an operating system based entirely off of web services? Plenty of reasons! The biggest boil down to the following points:
  • No need to back up local data (for the most part) - Everything you need is already in the cloud!
  • No need to run cumbersome anti-virus software, as everything you are doing is online, you are only running a web browser (and plugins) on the local machine, nothing else.
    • This does, however, place a higher emphasis on staying safe from phishing sites.
  • Cheaper computers! If the only requirement is the ability to run a web browser, the hardware needed is relatively cheap to manufacture. No need for expensive components and upgrades. All the power you need is on the web.
The next post out will concern the hardware and physical feel of the CR48 notebook and my opinions on the design and build quality. Stay tuned!

Sunday, September 12, 2010

Kubuntu: The Perfect Middle Ground?

I really really like Kubuntu 10.04. Out of curiosity, I loaded up Kubuntu 10.04 onto my external hard drive to give it a spin. Other than loving the fact that I have my own personal encrypted Linux install bootable at all times on just about any computer I happen to be near, I really really like the new KDE. Take the easy-to-use mentality of standard Ubuntu and mix it with the endless-options power-user mentality of KDE and you get Kubuntu. First impressions went something like this:
Oh! Its the ease of Ubuntu! But wait... all of these options.. all of these rolled in configuration options, right up front? This is made for power users! But it is still Ubuntu? I'm confused... and happy...
Kubuntu seems like the perfect middle ground for those not yet happy to jump to Fedora, SuSE, or Debian proper. Kubuntu still contains some helpful Ubuntu-centric additions (read: training wheels) for the Linux newcomers, but maintains the features and customizations that power-users crave. To add to the list of things I really like about Kubuntu, it is absolutely beautiful.
If I were to pick one Linux distribution to deploy to a mass enterprise environment, it would be Kubuntu. Debian backend, Ubuntu ease-of-use, and KDE power and flexibility. It could possibly be one of the best general office use distributions yet.
The only problems I can see with KDE is operating within a current Microsoft-rich environment (and this is more of a general Linux /OpenSource problem than a KDE/Ubuntu problem) is the total lack of Exchange support. Whether it is with Evolution or Kontact, it just kills me when I find amazing open source applications that don't work with the biggest force in business today. If running a business on open standards and open technologies is interesting to you, consider Kubuntu a powerful choice.
I highly recommend Kubuntu for those who are ready for more Linux power in their hands, while not quite ready to take the full plunge.

Saturday, August 7, 2010

Server-Bits #9: Public Key Authentication in SSH or Passwords are Boorish

In this Server-Bits tutorial, I'll show you a real time-saver when it comes to SSH and anything connected to SSH. To put it simply, public key encryption in SSH is where you don't need to log into an SSH account because the public key (stored on the server) matches your private key (stored on the client machine), and it logs you into your account. Because anyone with your private key can appear to be you and gain access to your account, it is extremely important to guard your private key with your life. The public key can float around the internet for all time without any danger to yourself, your accounts, or your private key, as public/private key encryption is very secure.

Thursday, July 22, 2010

Test Post from GoogleCL

This is a short test post to see if GoogleCL will do exactly what I want from the command line. I do have multiple blogs that I mangage through Blogger... Hopefully this posts to the correct one.
Edit: It works!!

Saturday, July 10, 2010

Fedora 13


Recently, I've changed Linux distributions to Fedora for my main netbook distribution. Coming from a pretty strict regimen of Debian/Ubuntu for a very long time (after moving from SuSE some years ago), I always had a fond love of Debian-based systems, so I was a bit wary about going back to RPM systems (especially after the terrible time I had dealing with YaST). I'm happy to announce that I really do like what Fedora 13 brings to the table. Installation was wonderful, even better than Ubuntu 10.04's install, and even YUM isn't too bad to work with. From the get-go, Fedora 13 let me have full-drive encryption, something that you only get with the text-based Ubuntu alternate installer. To satisfy my full-drive-encryption requirement, I had to fight with the alt-installer for Ubuntu for quite a bit before I worked out a complicated workflow to get all the partitioning set up just the way I like it. Needless to say, it was a total pain in the ass to get working just right with Ubuntu. Just the opposite experience with Fedora 13, it was painless and easy, using the "Standard" installer, Fedora's install just gave me an encryption radio-button and all the necessary dialogs.
Using the system is just as much of a joy. You get a standard Gnome desktop, as usual, but with a bit more focus on enterprise options and business-like settings. With Ubuntu being the most widely-used Desktop distribution, the majority of development will done on that platform, which made some software utilities a bit different to install, but absolute worst case: You download the code and compile it yourself. Not too complicated at all. Fedora seems to run with a bit of a speed-boost as well. Ubuntu always felt like it was dragging its feet on my netbook, but I've had just the opposite reaction to Fedora 13: It really is quite speedy. Linux distributions are all a bit fuzzy in how different they really are from each other, but in my mind, that's a positive point. I don't have to re-learn everything, I can take what I've done with my customized Ubuntu boxes and apply the same theory and logic to Fedora. Having distributions built on one standardized kernel is what makes Linux great.
Bottom Line: If you're looking for a bit of a change in your daily use, want a speed-boost, or are looking for really easy encryption options, give Fedora 13 a shot, you'll be glad that you did.

Wednesday, June 2, 2010

Google Moves Away from Windows

So, word has been getting around that Google is officially dropping support for Microsoft Windows internally. Computers running Microsoft Windows are going to be phased out for Linux and OSX machines. Honestly... Who didn't see this coming?
Google has stated many times that the default operating system for Googlers is a heavily modified Long Term Support (LTS) version of Ubuntu Linux, affectionately named "Goobuntu". While this modified distribution has never been released outside of Google, it is in wide use and support there, and hardly a secret. That said, Windows machines aren't being done away with entirely, Google has stated that employees that really need to use Windows can acquire special permissions to use the operating system. Lets take this from a fresh angle: If all you really know how to use is Windows, you probably shouldn't be working at Google.
Lets think logically about what Google really needs Windows machines for: Windows development. Sure, they have Picasa, Desktop Search, Earth, and a few other cross-platform apps that they need to build and test on versions of Windows, but these things can easily be accomplished inside a virtual environment. The vast majority of Google's focus right now is split between Chrome OS (Linux), Android (Linux), and the web, and if recent trends have shown us anything, its that Google is interested in moving away from desktop applications altogether. Google has proven that they can take big technologies and move them to the web, and that's exactly what they are focused on. Microsoft's mission used to be "A computer on every desk and in every home, running Microsoft software.", and Google has taken a much more open stance in theirs, what their mission should be is: "A browser on every device, with every person, using Google products."
If Google were a software company first-and-foremost, this would be a huge deal, but they just aren't. Google is focused on providing platforms and services for other people to utilize and build on. Android development tools exist for every platform, and, from a personal point of view, development on Linux platforms tend to be much nicer than Windows or OSX. By keeping Apple machines around, Google is showing that they will still be developing applications for the iPad and iPhone. This is extremely important. Google doesn't want to limit who can use their products, so having a presence on their biggest competitor's device is a wonderful strategy. Google isn't interested in limiting themselves, and being browser-based is the cornerstone of their ideals.
It does seem like Google is setting a precedent for other companies as well. Showing other technology businesses that they can be free from licensing and closed, bug-ridden software. If one of the biggest technology companies in the world can do without Microsoft Windows, anyone can. This move to make their unreliance on Windows official and public seems like a power play to the rest of the industry, setting an example and forging the first path away from Windows. I'm all for more businesses relying on Linux, it will do huge amounts of good for the open source ecosystem and mentality.
Like I said before, I'm really floored that people are surprised over this, everyone should have seen this coming. Only time will tell if other companies are willing to follow Google's example and give up their Windows addiction.

Original Engadget post

Tuesday, May 4, 2010

Server-Bits #8: TrueCrypted Home Directories or SHROUD

So, I've completed work (a while ago... was still gathering the time necessary to write this blog post) on Project: SHROUD (Link defunct for now...) and it is time to release the documentation on how I've put it together. The pieces have been floating around the internet for some time, but I'm here to put this in one central location so you can have it up and running in no time flat.

But what exactly is Project SHROUD?
From the PastaNet blog: "Completely encrypted storage space via PastaNet using TrueCrypt and SSH. Hosted on an encrypted RAID-5 server and stored in your own personal encrypted volume, your data is not only safe, but extremely secured. Your personal file volume is dismounted 60 seconds after you disconnect, leaving your data completely encrypted (Twice over!!). Completely secured network access through SSH encryption. You can access your SHROUD drive through any FTP program that supports SFTP (The vast majority of these programs do) or by mounting it as a network drive through ExpanDrive (working on alternatives for this) [Linux users need not apply, as mounting SSH volumes is built into the OS]. Completely encrypted, completely secured, cloud-based storage."

See the full article after the jump.

Saturday, May 1, 2010

Server-Bits #7: Transmission and Web-Controlled Torrents


Have you ever been away from your machine when you've thought to yourself, "Oh! I need to torrent *COMPLETELY LEGAL CONTENT HERE*!! I wish I was at my machine...". Now you don't have to be at your computer, you can control all of your torrents, and add new ones, entirely through Transmission's web client.

Transmission should be installed on Ubuntu by default, but just in case it isn't, you can install it by running the command:
sudo apt-get install transmission
Go ahead and start this in GUI-mode. Just open Transmission while you are logged into Gnome. From here, go to: Edit -> Preferences. Navigate to the Privacy tab. There are a few options that NEED to be changed.


First off: Blocklist. Blocklist. Blocklist. Enabling the blocklist will keep the vast majority of anti-P2P groups off of your back. Make sure that you enable automatic updates as well. The next thing you need to change is the encryption. Change this to Encryption Required. This will ignore and close any connection that is not masked by encryption.


Next, in the Network tab, check the "Pick a random port every time Transmission is started" box.


In the Web tab, check the "Enable web client" box, change the listening port to whatever you prefer (and forward the port on your router if you so choose [forwarding this port will give you the ability to manage your torrents outside of your network]). Make sure "Use authentication" box is checked and choose a username/password. If you would like, you can also restrict access to certain IP Addresses. This is helpful if you are only going to be accessing this page from a known machine with a constant known address.


Now, in a web browser of your choice, navigate to 'YourHostname:YourTransmissionPort' and you should be greeted by a popup login box. Enter the username/password combination that you set up and start remote torrenting!!


Sunday, April 18, 2010

Server-Bits: Tip #2

Just a cool tip I found to hide the user list on the logon screen. I have a great number of users, and the list was getting pretty ridiculous... This command will restart your xserver. Save your work beforehand.
sudo gconftool-2 --direct --config-source xml:readwrite:/etc/gconf/gconf.xml.mandatory --type Boolean --set /apps/gdm/simple-greeter/disable_user_list True

sudo /etc/init.d/gdm restart


And that will give you a nice clean username/password box.


Via: Ubuntu Geek: http://www.ubuntugeek.com/how-to-remove-hide-users-list-at-login-screen-in-ubuntu-9-10-karmic.html


Friday, February 26, 2010

Server-Bits #6: Duck and Cover or: Protecting your users with VPN

In this world of turmoil, uncertainty, and Wireshark, web browsing in a public place is like putting on an 80's hair metal concert, completely unsafe and everyone can see what's going on. Unsecured wifi access points (And even those secured, but using older protection) will show a great deal of your traffic in plain text to anyone who loads up a program and 'sniffs' the air. Too embarrased about still using Friendster? Then set your server up as a VPN proxy and route all of your traffic through encrypted SSH. Completely secured internet, on all of those untrusted networks. What are you waiting for? Get to it!

  1. The first thing to do is set up a new user account that will only have VPN access. - 'sudo adduser vpnbuddy' (You can set this up with any user account you wish)
  2. Set up a new password for the user account (Make sure it is a lengthy/complicated password, the user will not be able to log in and change it.
  3. Next, we need to disable shell access for this account. We can change shells in /etc/passwd - 'sudo nano /etc/passwd'
    1. NOTE! This is if you would like the user to have only VPN access, for standard SSH accounts, you don't need to change anything on their account, VPN is already available to them.
  4. Navigate to the bottom of the file, to the line with the new username, go to the end of the line and change the '/bin/bash' to '/bin/false'.
  5. Ctrl+O to save, hit enter.
  6. Ctrl+X to exit.
That should be all the server-side work you have to do. With SSH already set and configured, your newly created VPN user is ready to go! But.... That's the easy part... Next, we have to work on deploying and setting up VPN for your new users.

Possibly the easiest way to accomplish this goal is to make a nice zip file of the things we will be building, and give people a foolproof way to set up their programs to take advantage of the secured connection.

  1. The first thing to do is go download Putty. Realistically, most of your users will be on Windows, so we need an SSH client to connect them over to your server and open up the VPN port. The perfect program to do the job would be Putty.
  2. create a new text file. You can do this in notepad, nano, gedit, Notepad++, whatever plain text editor you please.
  3. You want to put this in your text file:


    putty.exe -N -D 8888 CLIENTUSERNAMEHERE@pastanet.homelinux.com
  4. Save the file as "Connect.bat"
  5. Make a new folder somewhere and put the 'putty.exe' file in it. Next, throw your new 'Connect.bat' file in it.
  6. Now... its time for some documentation... One of the slowest parts of running your own server. Yes... we all know you know how to connect to SSH and make everything just work, but your users need you to hold their hands as they walk through this desolate land of technology. Take a look at the documentation I've given my users...(Google Docs Link)
    As you can see, its easy to understand, easy to distribute, and in a format that most anyone can open (PDF).

  7. Now users need to set up FireFox and Pidgin to use the VPN access. You can head HERE to run through the Flickr screenshot tour of setting up FireFox and Pidgin (Feel free to take my screenshots/documentation and use it for your own server, everything I make is under a free-to-share Creative Commons license) 
  8. After that, the only thing that is left is to acquire users and remain encrypted online. VPN works wonders for thwarting wifi eavesdroppers, suspicious network admins, and poorly built web filtering software. Have fun with it!
Again: Sorry this took so long to publish, its been a great deal of work getting all of the documentation kinks worked out. Its a bit difficult to make things perfectly easy and usable for standard users, and while running your own server, you'll figure that out as well. Next up: Remote torrent administration with Transmission.

Monday, February 15, 2010

Server-Bits: Interlude

I really have been working on the next set of posts, really... For two weeks. The next post will include something equally different, but just as important as sheer technical skill: The ability to work with users. Deployment, documentation, dumbing-things-down. If you always count on the super-nerdy to use what you build, you won't go very far, things need to be documented and easy to use. Stay tuned, there is a lot to go through.

Saturday, January 16, 2010

Server-Bits #5: Sockso Music Server and the Joys of SSL


Sockso!! Sockso is a music streaming server program. It will take into account any folders you have on your computer, index the music from them, then create an online-accessible database which you can stream from. Your entire music collection: Working anywhere the internet and flash will. Lets get started:
  1. Head over to http://sockso.pu-gh.com/ and download Sockso. If you're running this through ssh, use this command to download it: wget http://sockso.googlecode.com/files/sockso-1.2.1.zip
  2. Then extract the files - unzip sockso-1.2.1.zip
  3. Then we'll move it to the /var directory - mv sockso-1.2.1  /var
  4. Next, we'll jump into the sockso directory - cd /var/sockso-1.2.1/
  5. But we can't run it just yet, we don't have the java runtime environment install on our server, but don't fret, its but a command away.
  6. sudo apt-get install openjdk-6-jre
  7. Now we can launch Sockso [This method of launching will launch Sockso with https forced and without a graphical interface, if you want to run unsecured or with a graphical interface, just remove either (or both) of those switches] - cd /var/sockso-1.2.1 && java -jar /var/sockso-1.2.1/sockso.jar "$@" --ssl --nogui
  8. Now you can type 'help' to see your choice of commands. Running Sockso through the terminal limits you in some ways, to gain the full feature set, plug in a monitor and check out the sockso GUI. [The easiest way of launching the Sockso GUI is by running 'sh /var/sockso-1.2.1/linux.sh]
  9. Now lets add a folder for Sockso to watch - coladd /home/username/Music/
  10. This could take a while to add to Sockso... When it adds a folder, it indexes all of the files into a database that it can then pull from.
  11. Next, we should add a user to the system - useradd username password emailaddress@hostnamehere.com
  12. The default port for Sockso is 4444, but you can change this with - propset server.port [port number]
  13. All of the settings can be shown with proplist and changed with propset.
  14. The only thing left to do now is test it! Head over to https://yourhostnamehere.com:4444 to test it out! [You must use https if you have --ssl enabled, otherwise, use http].
  15. I recommend using the commands "propset users.disableRegistration yes" and "propset users.requireLogin yes" to lock down your media streaming to only those users you specify, but this is up to you.
  16. Have fun streaming!

One of the cooler parts about running a linux box is the ability to add things to what's called your  .bashrc file. This file can do anything from setting environment variables, to running a startup command when you log in, to setting program aliases. We we be doing the latter with Sockso. The command to run Sockso securely is long, arduous, and complicated, by adding a single line to the .bashrc file, we'll turn this command into a single word. [NOTE: You will have to restart your bash session for the changes to take effect. This means either logging out of ssh and logging back in, or closing the terminal and opening a new one.]


To add a line to your .bashrc file, use the following command: echo "cd /var/sockso-1.2.1 && java -jar /var/sockso-1.2.1/sockso.jar "$@" --ssl --nogui" >> ~/.bashrc


Ok, let me explain this one.. The echo command just throws text on the screen, but it can also be used with a redirect to throw text in a file as well. Right now, you are throwing that big long command in quotes into the file ~/.bashrc. "~" or "Tilde" is a very short way to say "My Home Directory" and the .bashrc is the text file located in your home directory. Now, the part in the middle of these two, ">>", this is output redirection. Instead of echo throwing text into the terminal, it will instead append that text into the file of your choice (in this case, your .bashrc file). Doubles (>>) will add the output to the end of the file, while a single redirect (>) will completely replace the file. You should probably be careful with this one. You can redirect output for just about any program in a bash shell, it comes in hand for many many things. For further reading on Bash Redirection head over here, a wonderful noobie-friendly post.

And that's it for Sockso. In the future, we'll be covering remote BitTorrent administration, URL-rewriting, and Wiki's!

Thursday, January 7, 2010

Server-Bits #4: Apache and Wordpress


In this tutorial, I'll walk you through how to get your server hosting webpages powered by Wordpress. Wordpress is the most powerful free blogging software suite out there. Powering everything from CNN and BBC blogs to 72pc.com [Shameless Plug], Wordpress is as easy as you want to make it, or as complex and extendable as you want it to be.

The first thing we need to do is install a web server and supporting server applications. Apache2 will serve up webpages, mySQL will contain the wordpress database and any posts you make, PHP will handle the web-side scripting needed by Wordpress.

For these commands, you should run these in a Bash shell, either via a terminal window or ssh.
  1. 'sudo apt-get install apache2 mysql-server-5.1 php5 php5-mysql'
  2. You should then make a password for the mySQL root user (The installer will automatically prompt you). Remeber: Passwords should be lengthy and complicated.
  3. 'wget http://wordpress.org/latest.tar.gz' - This will download the very latest build of Wordpress to your home directory.
  4. 'sudo mv latest.tar.gz /var/www' - This will move the tarball (This is essentially the linux equivalent of a zip file) to the directory /var/www.
  5. 'cd /var/www' - This will change your current directory to /var/www.
  6. 'sudo tar xvvf latest.tar.gz' - This will extract the contents of latest.tar.gz.
  7. 'sudo mysql_install_db' - This will install the database platform on your machine.
  8. 'sudo mysql -u root -p' - This will bring you to the mysql prompt logged in as root.
  9. 'CREATE DATABASE wordpress;' - This will create the wordpress database we will later use.
  10. 'CREATE USER [enter your own username here];' - Creates a database user with the name you specify. Remember this username!
  11. 'SET PASSWORD FOR [your username] = PASSWORD("[enter your own password here] ");' - This will set a password for the user you just created.
  12. 'GRANT ALL PRIVILEGES ON wordpress.* TO [your username]@localhost IDENTIFIED BY '[enter your own password here] ';' - This will grant the user you just created privileges to do whatever he/she wants on the wordpress database.
  13. 'exit' - I think this command is self explanatory.
  14. Next, open up FireFox and, if you are on your server, go to http://localhost/wordpress/wp-admin/install.php, otherwise use http://your.domain.com/wordpress/wp-admin/install.php.
  15. The database name should be wordpress by default, so you shouldn't have to change this. Fill in your username and password (The one you created at the mySQL promp), you can leave the Database Host and Table Prefix at their default values.
  16. Log in with the randomly generated password, then change the admin password to something you will remember easier.
  17. For security purposes, you should create a new wordpress user and use that to post.
  18. To finish the install procedure, we need to change file permissons to be viewable externally. Run the command 'sudo chmod -R 755 /var/www/wordpress/'.
  19. In FireFox, navigate to http://localhost/wordpress/. You should see the front page of your blog pop up!
Now... Wordpress is one of the most extendible  platforms on the web, you can re-theme it, add plugins and widgets, control how editors/authors/readers interact with your page, and a ton of other stuff.
For themes, go here, for plugins, here.
Now for the most important part: Content. Get to writing, building, posting, uploading content that people will care about. This is now a public facing web-server (As long as you have forwarded port 80), so get to building!

Thanks to Jonathan Moeller for parts of this guide!


Tuesday, December 29, 2009

Server-Bits #3: Setting up SSH


Now that you have a server built, the first thing we need to do is get SSH set up. SSH will allow you to remote control your computer from anywhere that has an internet connection. You will need to forward port 22 on your router if you want to hit it from the outside.
  1. Just a reminder: Make sure your user password is lengthy and complicated. The last thing you want is for someone to waltz into your machine using the password 'password'. SSH will give an attacker direct access to your entire machine. While it is an extremely useful tool, it can be utter hell if misued.
  2. Next, open up a terminal. The command you want is 'sudo apt-get install openssh-server'.
    Now wait patiently for the program to finish installing.
  3. If you'd like to test SSH, use the command 'ssh localhost', ssh should ask you if you would like to trust the server on the other end, then it should ask you for your password.
  4. You have just established an SSH connection to your server. Congrats.
  5. A few things to keep in mind about SSH: To give someone SSH access to your computer [Known as giving someone a Shell Account], you would create a new user as you would usually do (either through the GUI or the command 'adduser'), and they are automatically granted SSH access.
  6. To establish an ssh connection, you will need a Terminal Emulator, the most popular program for Windows is called PuTTY. On any Linux or Mac OSX machine, you can just open up a terminal and type 'ssh username@host.com' to connect (You will be using your DynDNS hostname). If your username was 'samurailink3' and your domain was 'google.com', you could use 'ssh samurailink3@google.com' to establish a connection.
    Note: You don't have to use a domian, IP addresses work as well: 'ssh samurailink3@64.233.169.105'.
Cool things to try:

  1. On machines that are running an X-Server (Most any Linux machine), you can remotely display graphical applications with '-X': 'ssh -X samurailink3@google.com', then I can run 'firefox', and the instance of FireFox over at google.com will be displayed on this screen. Note: This is stupidly slow. Really really slow. But it is secure.
  2. SSH tunneling to secure otherwise insecure protocols (We will get into this in a later tutorial).
  3. SFTP: You can use most any FTP program (Such as FileZilla) to easily transfer files to and from the host machine [Just make sure to specify port 22!].
  4. If you want to set a pre-login banner to SSH, create a new text file [/etc/ssh/banner] and put any text you would like in that file, save, exit your text editor {Protip: You can use the command 'nano' to edit text in a terminal, you can then use Ctrl+X to exit to editor, answer yes or no to whether or not you would like to save. Example: 'nano /etc/ssh/banner'}. Now, edit your sshd config file [/etc/ssh/sshd_config] and add the line 'Banner /etc/ssh/banner'. Save and exit. Next time you attempt to log into SSH, you will be greeted by whatever text is in /etc/ssh/banner!
  5. If you would like to set a post-login message to SSH, (On Ubuntu 9.10), you must first disable update-motd. You can do this by running 'sudo update-motd --disable'. Then edit the text file [/etc/motd] to say whatever you want. When a user successfully logs into SSH, they will see whatever is in this text file.
  6. Remember: If you change any configuration, restart your SSH server with this command 'sudo /etc/init.d/ssh restart'. {Protip: Changing a configuration file for a service in Linux doesn't mean you have to restart your computer, that's the Windows way of thinking. The vast majority of the time, all you need to do is restart the service. These scripts are located in /etc/init.d/. We will cover them when the time is right.}
For now: Enjoy remote administration of your machine!

Wednesday, December 23, 2009

Server-Bits #2: Routers and DynDNS


Ok! Now that you have a working Ubuntu box, we need to forge a path to get to it from the outside. This tutorial will be... well.. completely and utterly useless unless you follow the next one. Especially the next one. The first thing we need to do is set up your router to forward ports. You should become extremely familiar with this process, as you'll be doing a great deal of port forwarding over the next few tutorials.
The first thing you will want to do is head over to PortForward.com, look up your router model, follow the general instructions.

The basic ports you should forward are:
  • 22 - SSH
  • 80 - HTTP
For now... This list will grow as we add more to your server.

Now... We need to get you off of that bare IP address, and onto a domain name. Sure, you could spend the $10 bucks a year to buy out a .com domain name, but this tutorial is based around the idea that you want to spend as little as possible. This is where DynDNS comes in. Head over to DynDNS.com and create yourself a free account. Go ahead and go to the "My Hosts" section and add a new hostname.

Now... this is the important part: Naming. Go ahead, no rules here, one of the most pivitol moments in creating your network will be naming your network. Service type can remain at "Host with IP Address", and go ahead and use your external IP address. You can leave "Mail Routing" unchecked for now. It will take a bit for the DNS records to propagate throughout the internet. I've had this process take 10 minutes, I've had this process take 4 hours. Just sit back, have a mug of coffee, and enjoy yourself, you are well on your way to having a workable server.

We will get to testing your domain in the next tutorials.

Still coming up:

  • SSH
  • Web Server (Apache2)
  • Wordpress
  • FTP
  • Streaming Music Server (Sockso)
  • Remote Bittorrent Administration (Transmission)
  • and more...